'GhostThread' Exploit Paralyzes Seoul and Singapore's Smart Grids
A novel zero-day exploit, dubbed 'GhostThread,' has brought two of the world's most advanced smart cities to a standstill. The attack on the ubiquitous QuantumMesh protocol reveals the catastrophic fragility at the heart of our connected future.
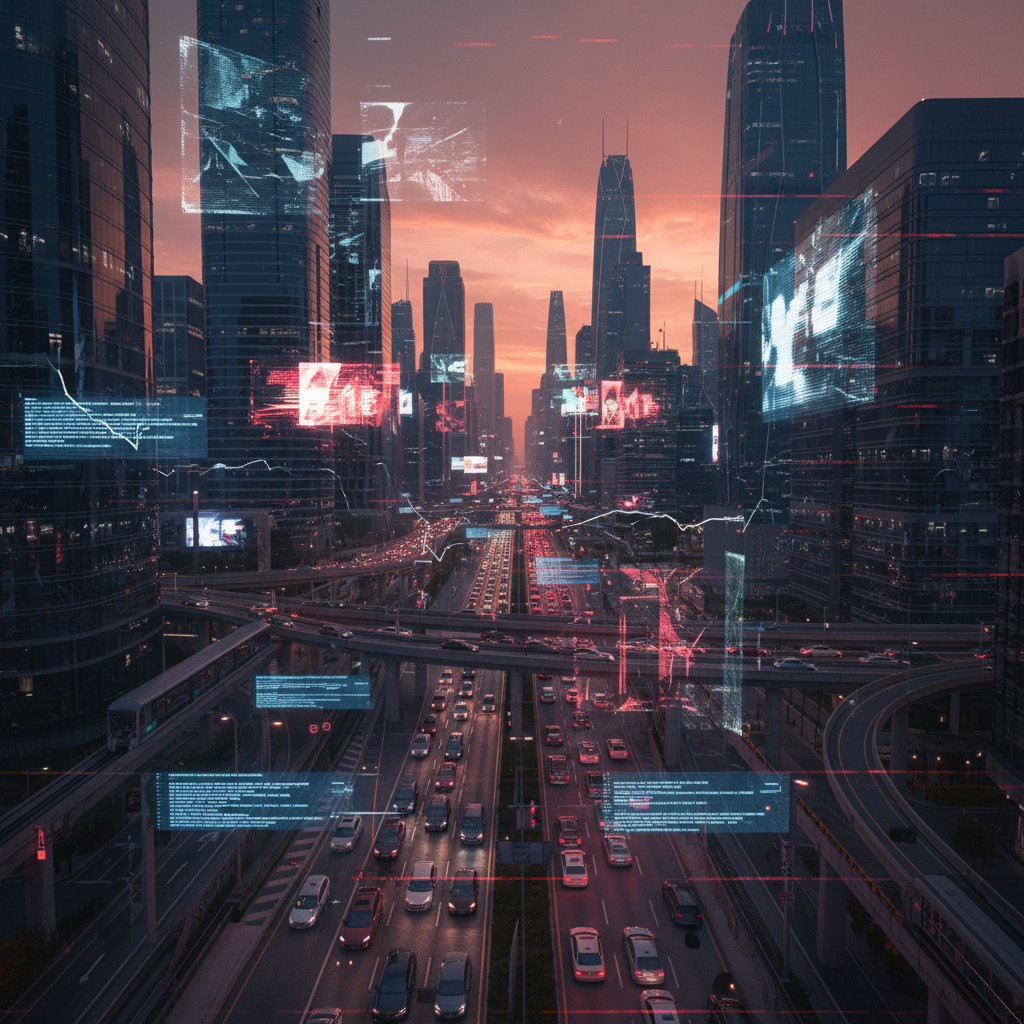
At 8:15 AM local time yesterday in Seoul, the city’s intelligent traffic management system went dark. Traffic lights froze, defaulting to red. Digital signage on bus routes flickered and died. Miles away in Singapore, controllers at the Marina Bay command center watched in disbelief as sensor data from the city-state’s water reclamation and public transit networks flatlined. This was no random outage. This was a coordinated, synchronous attack that exploited a devastating vulnerability in the very fabric of the modern smart city: a zero-day exploit in the ubiquitous QuantumMesh IoT protocol, now codenamed 'GhostThread'.
What Happened: A Synchronized Shutdown
The morning of September 24, 2026, will be remembered as the day the smart city dream became a logistical nightmare. The attack vector was QuantumMesh, a low-power, wide-area networking protocol governed by the international Ubiquiti Alliance consortium. It has become the de facto standard for connecting billions of non-critical but essential IoT devices—from traffic sensors and smart meters to environmental monitors and public information displays.
In Seoul, the primary impact was on the T-money integrated public transport system and the TOPIS traffic control network. Automated buses halted mid-route, unable to authenticate with their next network node. The city’s complex, multi-level road network descended into gridlock as every signalized intersection failed. In Singapore, the attack targeted the PUB water management system, halting real-time monitoring of the NEWater reclamation plants, and disabled the Land Transport Authority's network of real-time transit trackers, leaving millions of commuters guessing.
Crucially, core utilities like the power grid and emergency services remained operational, as they typically run on more robust, isolated SCADA systems. But the 'soft' infrastructure that governs urban efficiency and quality of life was paralyzed. The economic cost is already estimated in the hundreds of millions of dollars in lost productivity, and the social cost is immeasurable. The attackers demonstrated that you don't need to cause a blackout to bring a city to its knees.
The Ghost in the Machine: Unpacking the Exploit
Cybersecurity firms, including Mandiant and CrowdStrike, working alongside South Korea's KISA and Singapore's CSA, have pieced together the anatomy of the attack. GhostThread is a sophisticated zero-day exploit targeting a specific flaw in QuantumMesh protocol version 1.7.2, the most widely deployed version.
The vulnerability is a classic race condition within the protocol's device authentication handshake. In simple terms, when a new device attempts to join a QuantumMesh network, it undergoes a security check. The attackers discovered that by sending two specially crafted authentication requests in rapid succession—within a nanosecond window—they could create a state of confusion in the network gateway. The first request would begin the handshake, but the second, malicious request would be processed before the first was fully validated, effectively tricking the gateway into granting the attacker's device network-level administrative privileges.
Once authenticated as a privileged node, the attacking device had the keys to the kingdom. It could issue network-wide 'shutdown' or 'reset' commands that legitimate devices were programmed to obey without question.
This is the 'ghost' in the machine: a phantom administrative node that appears legitimate. From there, the attackers could broadcast authenticated shutdown commands across entire segments of the city’s IoT network. The elegance of the exploit is its subtlety; it doesn't break the system, it uses the system's own rules against it.
Why It Matters: The Fragile Backbone of the Smart City
The GhostThread incident is a brutal wake-up call. For years, the tech industry and urban planners have evangelized the benefits of standardization in IoT for building smart cities. A single, interoperable protocol like QuantumMesh promised efficiency, scalability, and reduced costs. Today, that standardization looks like a single point of failure on a global scale.
"We've built these incredibly complex urban organisms on a foundation of assumed trust in commodity hardware and software," says Maria Petrova, CTO of cybersecurity firm SentinelOne, in a statement to ByteWave. "GhostThread proves that a single flaw in a 'non-critical' protocol can cascade into systemic failure. We traded resilience for convenience, and the bill has just come due."
The incident highlights a critical philosophical divide in infrastructure design. While the internet was designed to be decentralized and resilient, many smart city IoT deployments have been implemented with centralized command-and-control architectures. When the central 'brain' is compromised, as it was here, the entire system fails. The reliance on a single protocol, QuantumMesh 1.7.2, meant there was no diversity to blunt the attack's impact. Every vulnerable device was a domino waiting to fall.
Attribution and Fallout: Enter the Silkworm Collective
While definitive attribution is notoriously difficult, a consensus is forming among intelligence agencies. The digital breadcrumbs—including custom malware compilers and unique command-and-control server techniques—point to a new, highly sophisticated state-sponsored threat actor dubbed the 'Silkworm Collective'.
Evidence suggests the group is state-sponsored and operating with geopolitical motives. The choice of targets is telling. Seoul and Singapore are not just technologically advanced; they are key economic partners of Western nations and symbols of stable, high-functioning governance. The attack wasn't ransomware or data theft; it was a pure power play. It was designed to cause maximum disruption with minimum permanent damage—a show of force intended to demonstrate a new type of asymmetric warfare capability.
The governments of South Korea and Singapore have issued joint statements condemning the attack as an act of 'digital aggression' but have stopped short of naming a specific state sponsor. Behind the scenes, diplomatic channels are electric as nations grapple with how to respond to an attack that exists in a grey area between espionage and an act of war.
The Road to Recovery: Patching a Trillion Devices
The Ubiquiti Alliance, the consortium managing the QuantumMesh protocol, released an emergency patch—version 1.7.3—within 36 hours of the incident. The fix addresses the race condition by introducing a locking mechanism that ensures only one authentication request can be processed at a time. But distributing the patch presents a monumental challenge.
The problem lies in the nature of IoT devices. Many are low-power, 'fire-and-forget' sensors embedded in concrete, buried underground, or installed in difficult-to-reach locations. A significant percentage lack robust over-the-air (OTA) update capabilities. Experts estimate that hundreds of millions of devices will require manual, physical updates—a process that could take months, if not years, and cost billions.
The Triage Process:
- Tier 1 (Immediate): Gateways and critical nodes with OTA capabilities are being patched first to restore basic functionality.
- Tier 2 (Months): Devices accessible for manual updates by city technicians. This includes traffic controllers, public transit modules, and accessible utility meters.
- Tier 3 (Years/Never): Embedded, non-essential sensors which may be deemed too costly to update and will simply be abandoned or left vulnerable.
This long tail of unpatched devices creates a persistent security risk. The GhostThread vulnerability will linger in our urban infrastructure for the better part of a decade, a ticking time bomb waiting for a less sophisticated attacker to reuse the exploit.
The silent, synchronized halt of two of the world’s most celebrated smart cities is more than just the biggest cyberattack of 2026. It marks the end of an era of naive optimism in IoT. The GhostThread incident has forced a global reckoning with the hidden risks of our interconnected world. Moving forward, the conversation around smart cities will no longer be solely about efficiency and convenience, but about resilience, security, and the profound responsibility that comes with wiring our world together. The ghost is out of the machine, and it will haunt our infrastructure decisions for years to come.
Frequently asked questions
Is my personal smart home device using the QuantumMesh protocol at risk?+
It's unlikely. The QuantumMesh protocol is designed for large-scale, low-power, wide-area networks used in industrial and municipal settings. Most consumer smart home devices use protocols like Wi-Fi, Zigbee, or Thread, which are not vulnerable to the GhostThread exploit. However, this incident serves as a good reminder to keep all your personal IoT devices updated with the latest security patches from their manufacturers.
Why were the power and water grids not taken down?+
Critical infrastructure like power grids, water treatment plants, and hospitals typically use more robust and isolated industrial control systems, often called SCADA. These systems are 'air-gapped' or have extremely limited, highly-monitored connections to the outside world. The GhostThread attack targeted the 'soft' layer of city management—traffic, public transit data, and environmental sensors—which uses more open, commercial-grade IoT protocols for efficiency.
What makes the 'Silkworm Collective' different from other hacking groups?+
Unlike ransomware groups motivated by money or hacktivists driven by ideology, the Silkworm Collective's actions point to state sponsorship. Their goal wasn't financial gain or data theft, but demonstrating capability. The sophistication of the zero-day exploit and the coordinated, multi-country attack require resources far beyond most criminal organizations. Their objective appears to be geopolitical signaling and demonstrating a new form of asymmetric warfare capability.
How can cities prevent this from happening again?+
Experts are recommending a multi-pronged approach. First, moving away from a monoculture of a single IoT protocol to a more diverse ecosystem to limit the blast radius of a single exploit. Second, implementing 'zero-trust' architectures where no device is automatically trusted. Finally, mandating that all devices used in critical or semi-critical city functions have robust, proven over-the-air (OTA) update capabilities to allow for rapid patching.
What does 'race condition' mean in simple terms?+
Imagine a security guard who has to check an ID and then open a gate. A 'race condition' exploit would be like two people rushing the guard at once. The guard starts checking the first person's ID, but before they can finish and make a decision, the second person shoves their (fake) ID in front of them and slips through the gate while the guard is confused. The attackers exploited a similar tiny window of confusion in the system's digital security check.
Liked this story?
Share it with a colleague, or explore more in the Cybersecurity section.
More stories
Rust’s Fortress Breached: Inside the ‘Ferrous Maelstrom’ Supply Chain Attack
Rust, the language prized for its security, is facing an ecosystem-level crisis. A sophisticated, state-sponsored attack on its central package registry has left thousands of companies scrambling to discover if their software is compromised. This is what happened.
The Web's Encryption is Broken: Inside QUIC-Sandman, the Bug Shaking the Internet
A newly disclosed vulnerability, QUIC-Sandman, allows attackers to bypass encryption protections in the internet's foundational QUIC protocol. We are now in a race to patch the web before widespread exploitation begins. The very trust model of our connected world is at risk.
ChronoLeap: The New CPU Flaw That Makes Spectre Look Like Child's Play
Researchers have disclosed ChronoLeap, a catastrophic new hardware vulnerability in modern CPUs. It threatens the very foundation of cloud computing and shared systems, forcing a painful trade-off between security and performance that will redefine chip design for a decade.